
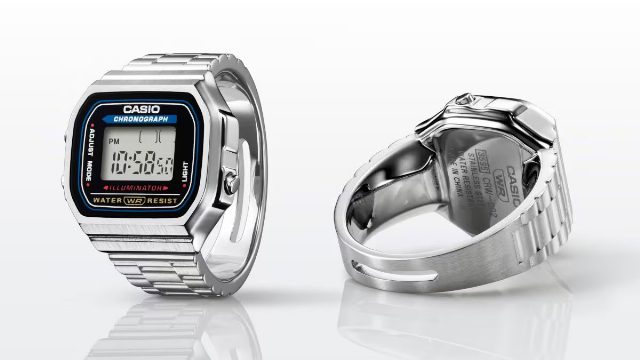
Casio’s cute digital ring watch just got a successor
Casio is back to deliver peak digital nostalgia straight to your finger.
Search
Results for "Cute".
Casio is back to deliver peak digital nostalgia straight to your finger.
The always-on AI agents can keep projects moving across your apps while you’re.
Technical details and a proof-of-concept exploit have been published for a new WordPress cross-site request forgery (CSRF) vulnerability dubbed 'Click2Shell' that affects the platform's Core component.
Check Point Software has released security updates to address a critical vulnerability that can let attackers execute code with root privileges on management systems.
A maximum-severity vulnerability in the GiveWP plugin for WordPress allows an unauthenticated attacker to execute arbitrary commands on the hosting server.
Hugging Face has launched a new robot called Microduck.
Pet owners, rescue agencies, and wildlife groups are calling for new safeguards as AI makes it harder to tell whether animals, from polar bears to house cats, are real or.
Check Point security gateways were targeted in PHP2Shell attacks that deployed destructive malware on VMware ESXi hosts, raising questions about a possible false-flag operation.
Check Point has released emergency hotfixes for a high-severity vulnerability that attackers have been exploiting since October to gain root privileges and establish persistence on vulnerable devices.
New worm-like malware SCKit targets MSPs, exploiting CVE-2026-84869 to spread from infected devices to MSP technicians' computers and compromise additional networks.
Hackers are actively exploiting newly disclosed N-able N-central zero-day vulnerabilities, including 4EverAble2Shell, to compromise servers and deploy cryptocurrency miners.
Apache HTTP Server has patched a critical vulnerability in the HTTP/2 module that could allow attackers to execute arbitrary code with server privileges, affecting versions 2.4.55 through 2.4.70 and standalone mod_h2 versions 2.0.8 through 2.0.42.
Endpoint management platforms are crucial for IT operations and security, but their administrative authority also makes them attractive targets for attackers. Learn how to protect against compromise and unauthorized access.
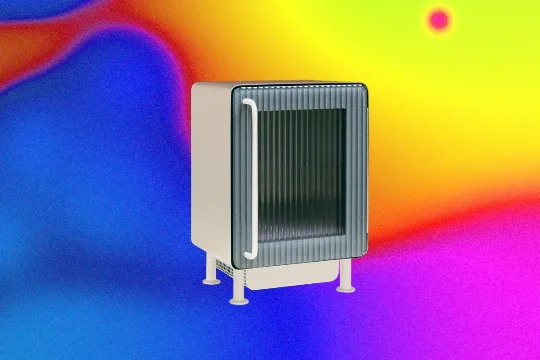
Rocco’s new Mini Mini fridge offers a stylish and affordable alternative to larger models, with impressive cooling capabilities and sleek design.
Turla hackers have deployed a new Cereal malware toolset to intercept emails on government Microsoft Exchange servers, according to cybersecurity researchers at ESET.
Hackers are actively exploiting the "SSHole" vulnerability (CVE-2026-123158) in OpenSSH to execute commands, steal credentials, and establish persistent access. [.
A former FBI agent was found guilty of stealing $2.5 million in cryptocurrency, highlighting the vulnerabilities in cybersecurity systems.
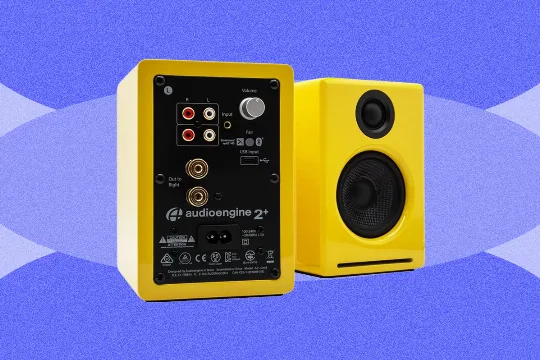
Discover the top computer speakers after extensive testing, from budget to high-end options.
Binance reveals how hackers exploited a trusted engineer to steal billions, highlighting the sophistication of cybercrime in the cryptocurrency sector.
Security researchers at Anthropic have developed an exploit for a critical Linux kernel vulnerability that allows unauthenticated attackers to remotely execute commands as root on servers running Multipath TCP (MPTCP) listeners. [.
A malicious version of Anthropic's Claude Code VS Code extension was distributed through Cursor's marketplace, exposing up to 5,000 developers to malware designed to install persistent SSH backdoors.
The US Cybersecurity and Infrastructure Security Agency (CISA) has confirmed that attackers are now exploiting a critical GitLab vulnerability, CVE-2026-97229, which was patched in early April.
Hackers quickly siphoned $6.3 billion from Binance in just 20 minutes, raising questions about the sophistication of the attack and the effectiveness of current security measures.
The Department of Education's use of the Malfoid meme is a disturbing example of right-wing propaganda in modern politics.
The critical flaw in UEFI firmware, used by most server vendors and data centers, allows attackers to execute code early in the boot process.
InfraTrust report highlights critical flaws in network devices, with PHP vulnerabilities posing significant risks.
Researchers discovered a malicious AGENTS.md file in a customer's Downloads folder that tricked an AI coding agent into installing a rogue npm package, potentially exposing sensitive information.
AI agents are becoming more autonomous and capable, but they also pose significant risks. Learn how to use them safely and protect your data with Gen's Agent Trust Hub.
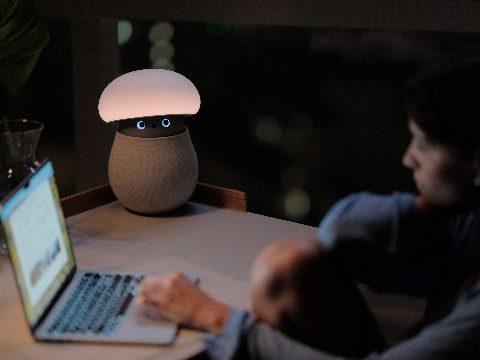
Meet Mori, a cute robot mushroom that doesn't really say (or do) anything, but reconnects you with nature through soothing sounds and gentle movements. Learn how this innovative product can enhance your home environment and reduce stress.
GitLab has released patches for a critical RCE vulnerability, CVE-2026-110264, and recommends immediate action to safeguard your servers. Here's how to protect your GitLab environment and avoid similar threats.