
AO3 Returns After Security Incident: Features Temporarily Disabled
After a security incident caused a temporary shutdown, AO3, the popular fan fiction forum, has announced its return with some features disabled to expedite functionality.
Search
Results for "Disable".
After a security incident caused a temporary shutdown, AO3, the popular fan fiction forum, has announced its return with some features disabled to expedite functionality.
A newly disclosed OpenSSH vulnerability dubbed "*sshole" allows attackers to log in to certain Alpine Linux and other musl-based Linux accounts that are configured to block password authentication, simply by entering an oversized password. [.
You can now linger on the Edge Panel peek window without worrying about freezing your screen with AI.
An Akira ransomware affiliate disabled the endpoint detection and response (EDR) solution on a compromised system by restarting the machine into Safe Mode with Networking.
The good news is that Google Messages is building its own in-app storage manager for selective data.
New AI toolbars and prompts are showing up in Google Docs and Gmail.
The Arch Linux project has temporarily disabled adoption of Arch User Repository (AUR) packages after a surge in malicious takeovers of existing packages.
A recent update made video playback the default for songs and podcasts with a visual component.

The Gentlemen ransomware-as-a-service (RaaS) is actively developing and maintaining a suite of endpoint detection and response (EDR) killers to help affiliates evade detection in attacks.

Maine has disabled its data breach notification portal after fraudulent disclosures were published, prompting a review of procedures to prevent future abuse.

Microsoft removed 73 repositories across its Azure, microsoft, Azure-Samples, and MicrosoftDocs organizations on GitHub, disrupting continuous integration pipelines.

A practical, in-depth guide on How to Disable Startup Programs in Windows 10 and 11 to Boost Boot Speed with concrete technical steps, security configurations.
New worm-like malware SCKit targets MSPs, exploiting CVE-2026-84869 to spread from infected devices to MSP technicians' computers and compromise additional networks.
Hackers are actively exploiting newly disclosed N-able N-central zero-day vulnerabilities, including 4EverAble2Shell, to compromise servers and deploy cryptocurrency miners.
Apache HTTP Server has patched a critical vulnerability in the HTTP/2 module that could allow attackers to execute arbitrary code with server privileges, affecting versions 2.4.55 through 2.4.70 and standalone mod_h2 versions 2.0.8 through 2.0.42.
Endpoint management platforms are crucial for IT operations and security, but their administrative authority also makes them attractive targets for attackers. Learn how to protect against compromise and unauthorized access.
Notion, the digital workspace platform, has disclosed that a security breach at its AI infrastructure provider, Fireworks AI, exposed customer chat transcripts in a limited number of workspaces, following a series of data breaches.
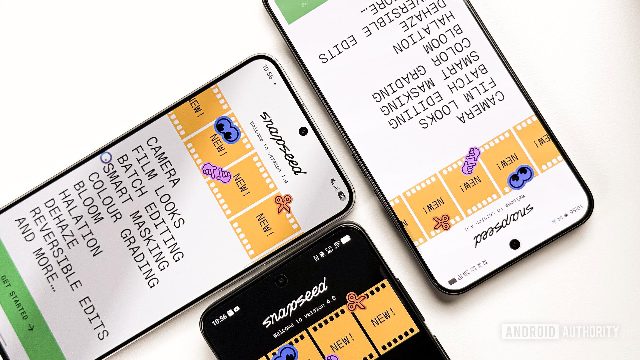
Snapseed introduces finer controls for image quality and Exif data, allowing users to customize export and save options.
Crédit Mutuel Arkéa bank in France was targeted in a cyberattack, resulting in $133 million in fraudulent transactions, affecting their systems temporarily.
DigiCert's data breach exposed customer and identity information, prompting a notification to affected users and review of identification documents.
Two Canadians face up to 10 years in prison for hacking US universities and mining cryptocurrency, with multiple universities affected.
New Jersey’s ebike law has caused confusion and decline in sales, affecting both disabled and everyday riders.
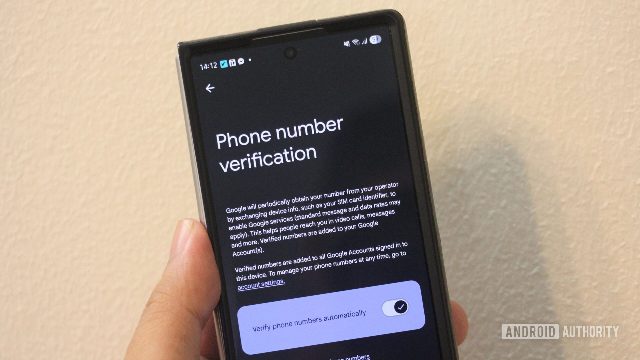
Google is silently linking phone numbers across your accounts. Discover the privacy risks involved and follow this guide to disable it.
Fintech platform Sageworks experiences an outage due to suspected cyberattack, impacting borrower-facing features.
Hackers have disrupted multiple European supermarkets, causing significant product losses and forcing managers to intervene. The attacks highlight vulnerabilities in IT infrastructure.
FBI confirms North Korean hackers as responsible for the largest cryptocurrency theft, affecting Binance.
Reddit plans to limit access to its full content to logged-in users to combat content scraping and improve ad targeting.
Prediction market platform Polymarket halts trading after a crypto-draining script breach, with $2.5M traced to a suspected attacker wallet and law enforcement involvement.
Discord will make public server discussions searchable on the web, improving accessibility and information sharing.
Chinese hackers use Silent Train framework to hide zero-day attacks targeting high-value systems, including critical infrastructure.