
Fake security tools on GitHub push backdoors and infostealers
Cybersecurity professionals are being targeted with infected security projects on GitHub that deploy a backdoor and information stealer malware. [.
Search
Results for "Github".
Cybersecurity professionals are being targeted with infected security projects on GitHub that deploy a backdoor and information stealer malware. [.
GitHub services are experiencing degraded performance, affecting Webhooks, Actions, and Pages. Learn how to troubleshoot and stay informed.
More than 17,000 fake repositories on GitHub are distributing the SmartLoader malware after the FakeGit campaign reactivated earlier this month to push the StealC infostealer.
More than 543,000 credentials exposed in public GitHub repositories were still valid in July despite the platform's security measures to prevent accidental leaks of sensitive data.
Two compromised GitHub Actions were re-enabled, pointing to malicious code for over a week, despite efforts to remove them.
An ongoing malware campaign uses SEO-optimized GitHub repositories to impersonate well-known software firms to push a previously undocumented information stealer called Rapuncel.
GitHub experienced a worldwide outage affecting multiple services, including API requests, Actions, Pull Requests, and authentication-related services. This guide provides a detailed look at the outage, its impact, and steps to mitigate the effects.
GitHub e PyPI introduziram um mecanismo baseado no tempo na ferramenta Dependabot para proteger contra ataques de supply chain e limitar seu impacto.
A large-scale operation dubbed 'FakeGit' is pushing SmartLoader and StealC malware through 7,600 malicious GitHub repositories that accumulated more than 14 million downloads.

A threat actor has published hundreds of fake GitHub repositories impersonating legitimate software and security projects to distribute infostealer malware.

ActiveState explains how GitHub Actions attack chains can evade traditional CI security scanners, why passing a scan doesn't guarantee a secure pipeline, and how organizations can better govern their CI/CD workflows.

An agentic coding tool tasked with cloning and setting up a seemingly benign GitHub repository could execute a malicious payload that remains invisible to security scanners, AI agents, and human reviewers.

GitHub has announced that npm v12, expected next month, will introduce several security-focused changes aimed at blocking supply-chain attacks abusing behaviors triggered by the 'npm install' command.

Microsoft removed 73 repositories across its Azure, microsoft, Azure-Samples, and MicrosoftDocs organizations on GitHub, disrupting continuous integration pipelines.

New variants of the NFCShare Android malware are being distributed as fake updates for legitimate banking apps hosted on GitHub.

A security researcher has released exploit code for a Visual Studio Code (VS Code) zero-day vulnerability that allows attackers to steal GitHub authentication tokens by tricking users into clicking a link.

A selected YouTube video about Online Tools, with context from GitHub and a practical checklist before watching.

A selected YouTube video about Online Tools, with context from GitHub and a practical checklist before watching.

A selected YouTube video about Online Tools, with context from GitHub and a practical checklist before watching.
Turla hackers have deployed a new Cereal malware toolset to intercept emails on government Microsoft Exchange servers, according to cybersecurity researchers at ESET.
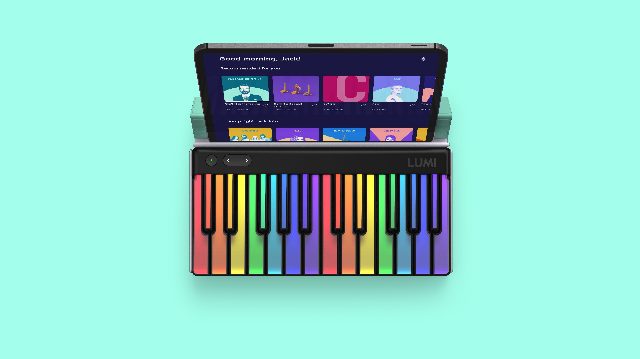
Roli, known for innovative touch-sensitive music devices, has collapsed, leaving customers with unpaid products and a community in turmoil.
Victoria Launcher offers a free, open-source alternative to Niagara Launcher, providing a streamlined home screen experience.
Researchers have uncovered a new Hugging Face malware campaign targeting GPUs for crypto mining, highlighting the evolving threat landscape in the AI space.
Machine speed attacks have become a significant concern, with attackers now enumerating data within 15 minutes of gaining access. This guide explores three common attack patterns and highlights the importance of effective detection and response.
OVHcloud's open-source CLI tool was compromised, leading to the distribution of malware that could steal developer secrets. This guide provides actionable steps to protect your systems and avoid similar incidents.
Coder's cloud development platform suffered an infrastructure compromise, leading to the delivery of malicious Terraform modules containing credential-stealing code.
Australian authorities have arrested two alleged TeamPCP hackers responsible for a series of high-profile supply-chain attacks targeting open-source software and developer platforms.
Multiple 'watermark removers' have surfaced days after Anthropic began watermarking text generated by Claude, including an open source project with over 4,500 GitHub stars and paid AI detection evasion services.
Mozilla announced today that it updated the GPG key used to sign Firefox and Thunderbird releases after it was accidentally exposed on GitHub.
LexisNexis has taken several of its services offline due to suspicious activity on servers managed by a third-party vendor. The company is investigating and rebuilding affected systems before bringing services back online.