
LinkedIn's New Feature: Stalking Protection or a Privacy Alert?
LinkedIn is testing a feature that alerts users to frequent profile views, potentially revealing stalking behavior or unwanted attention.
Search
Results for "Linked".
LinkedIn is testing a feature that alerts users to frequent profile views, potentially revealing stalking behavior or unwanted attention.
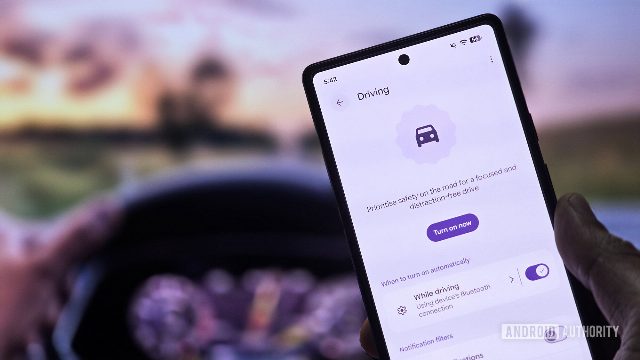
A new study shows how phone-related injuries are on the rise, with walking while using a phone topping the list.
A fake cryptocurrency trading app called Padre Terminal, previously available on the Apple App Store for iOS devices, has been linked to the theft of approximately $23,000 from 27 Solana wallets. [.
A law firm associated with Elon Musk has created a new organization promoting election integrity aligned with Trump’s false claims of election fraud.
The short-lived White House press secretary was listed as an adviser to a Kristi Noem, linked company that aims to use AI for mining. Both the company and she say she never worked there.
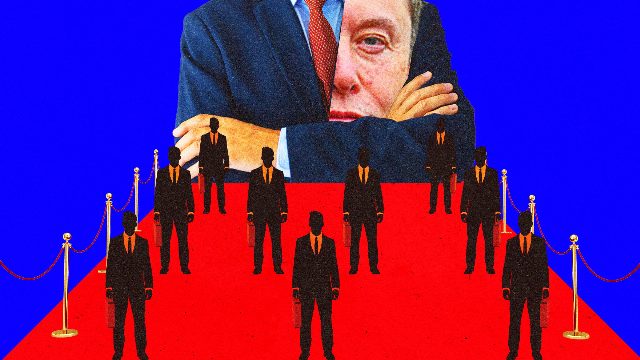
A newly formed nonprofit is reportedly funding and employing staff at the National Design Studio, raising questions about government transparency and AI integration.
220 million traveler records, including passport numbers and flight details, exposed through security misconfigurations in a Vietnamese-linked API system.
Australian authorities have arrested two alleged TeamPCP hackers responsible for a series of high-profile supply-chain attacks targeting open-source software and developer platforms.
A news reader, a movie recommender, and an important Linux release also feature in this new AI apps and services roundup!
Recent cyberattacks targeting hedge funds and private-equity firms have been linked to the UNC6671 extortion group, reportedly associated with the BlackFile threat actors.
A vulnerability in COLDCARD hardware wallet firmware allowed attackers to steal an estimated $88.6 million in Bitcoin from thousands of wallets whose seeds were generated using a flawed random number generator.
Iran-linked hackers have targeted Minnesota water and wastewater utilities, causing disruptions that have reached multiple sites.
Despite the ongoing AI boom, LinkedIn is holding the line on compute spending.
Iceberg lettuce, once synonymous with healthy eating, is now linked to a major outbreak in Michigan, raising questions about its safety and risks.
Cosmetics giant Estée Lauder warns of data breach involving personal information of employees, linked to a flaw in Oracle E-Business Suite.

UK authorities have charged five individuals in connection with the Russian Coms call spoofing platform, which was used by criminals to make over 1.8 million scam calls, resulting in financial losses for an estimated 170,000 victims.

The massive FortiBleed credential theft campaign has been linked to the INC and Lynx ransomware operations, suggesting the stolen Fortinet credentials were intended to fuel future network intrusions.

Nissan is warning that it suffered a data breach affecting current and former employees after threat actors exploited an Oracle PeopleSoft vulnerability in data theft attacks previously linked to the ShinyHunters extortion group.

A new backdoor dubbed Mistic has been observed in financially motivated attacks targeting organizations in the insurance, education, IT, and professional services sectors.

Klue suffered an OAuth breach that allowed 'Icarus' threat actors to steal Salesforce CRM data from multiple organizations in an ongoing extortion campaign, with Salesforce disabling the Klue Battlecards integration as a precaution.

Microsoft has fixed a known issue that caused Windows updates released since May 2025 to fail when installed via the Windows Update Standalone Installer (WUSA) from a network share.

The JDY botnet, a malware network previously associated with Chinese threat actors like Volt Typhoon, has significantly expanded its targeting scope and reconnaissance efforts.

Financial crime investigators in the Netherlands arrested two men and seized 800 servers linked to a web hosting company that enabled cyberattacks, interference operations, and disinformation campaigns.
US authorities have dismantled the FaceStealer campaign, a North Korean operation responsible for over $400 million in cryptocurrency theft, using sophisticated social engineering tactics.
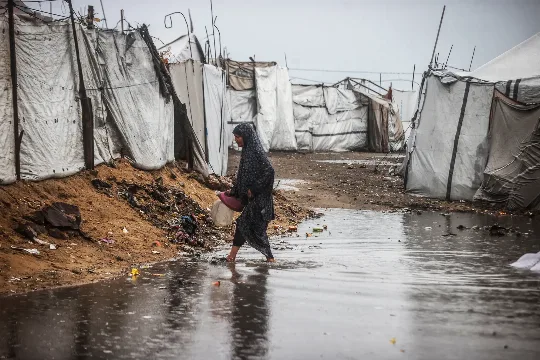
As Gaza faces flooding, municipal teams struggle to balance water supply and sewage management, highlighting the challenges of limited resources in disaster-stricken areas.
Microsoft confirms recent Windows updates are causing SQL Server performance and stability issues, particularly with linked server queries using OLE DB providers to external databases.
Baker Tilly has notified clients of a data breach involving personal information, with details on affected clients and data types yet to be disclosed. The breach occurred on a third-party platform used by Baker Tilly for client services.
ConnectWise is investigating an active malware campaign targeting managed service providers (MSPs) that uses compromised ScreenConnect environments to deploy rogue remote-access clients, impacting dozens of organizations.
Michigan residents approved a ballot measure limiting utility and contractor political donations. Now, utilities are suing over First and 14th Amendment rights.
Turla hackers have deployed a new Cereal malware toolset to intercept emails on government Microsoft Exchange servers, according to cybersecurity researchers at ESET.