
Fake Arch Linux packages push malware with root privileges
A threat actor uploaded malicious packages to the Arch User Repository (AUR) that impersonated two popular helper tools, yay and paru.
Search
Results for "Packages".
A threat actor uploaded malicious packages to the Arch User Repository (AUR) that impersonated two popular helper tools, yay and paru.
An ongoing npm malware campaign involving the 'indexed-btree' package shows how threat actors bypass supply chain defenses by hiding malicious code in a package's normal runtime behavior rather than in installation scripts.
Self-propagating malware named 'ChainDrop' has compromised more than 1,300 packages with a combined 2 billion monthly downloads on the Node Package Manager (npm) registry.

Five malicious versions of AsyncAPI packages were published to the Node Package Manager (npm) in a supply-chain attack that delivered a remote access trojan with info-stealing capabilities.

A campaign active since last November has been targeting Python developers building Telegram bots with trojanized Pyrogram forks that allow attackers to read arbitrary files on compromised servers.

More than 400 packages in the Arch User Repository (AUR) are distributing a Linux rootkit and infostealer malware targeting credentials and access tokens.

Hackers compromised 19 packages on the PyPI, collectively downloaded hundreds of thousands of times, in a new Shai-Hulud supply-chain attack that delivered malware designed to steal developer secrets.

Next-generation travel eSIM providers like Yesim are solving the problem of traditional roaming, which is clunky and opaque. Learn how eSIMs offer a more predictable and user-friendly alternative for modern digital travelers.

A new supply-chain attack has infected 36 packages on the Node Package Manager (npm) index with infostealer malware called IronWorm.

More than 30 npm packages under Red Hat's '@redhat-cloud-services' namespace were compromised in a supply-chain attack that distributed a new variant of the Shai-Hulud credential-stealing malware, dubbed "Miasma.".

A supply chain attack targeting the Laravel Lang localization packages has exposed developers to a sophisticated credential-stealing malware campaign after attackers abused GitHub version tags to distribute malicious code through Composer.
Bitdefender Antivirus Plus offers a solid antivirus solution at competitive prices, making it a valuable choice for users seeking reliable protection without the added features of more expensive bundles.
Researchers discovered a malicious AGENTS.md file in a customer's Downloads folder that tricked an AI coding agent into installing a rogue npm package, potentially exposing sensitive information.
LiteLLM, a popular open-source Python SDK, was compromised by hackers who pushed malicious Docker images containing malware. Here's how to secure your use of LiteLLM and protect against similar supply chain attacks.
OVHcloud's open-source CLI tool was compromised, leading to the distribution of malware that could steal developer secrets. This guide provides actionable steps to protect your systems and avoid similar incidents.
Election offices across multiple states have been targeted with suspicious letters, leading to evacuations and emergency room visits. This guide offers practical advice to ensure your office remains secure during the election process.
Get a 180-degree view, night vision, and two-way talk for $49.99 with the Arlo Video Doorbell 2K.
Law enforcement agencies from Latin America and Europe collaborate to arrest 95 suspects in a CSAM crackdown, highlighting the urgency of cross-border cooperation.
Meta Muse offers a user-friendly AI agent that excels in tasks like personal RSS feeds and product searches, making it a valuable addition to your tech toolkit.
Amazon offers a significant discount on Arlo's flagship 2K video doorbell, making it an attractive option for smart home upgrades.
Two compromised GitHub Actions were re-enabled, pointing to malicious code for over a week, despite efforts to remove them.
North Korean hackers infected over 30,000 devices worldwide, stealing over $10 million in cryptocurrency.
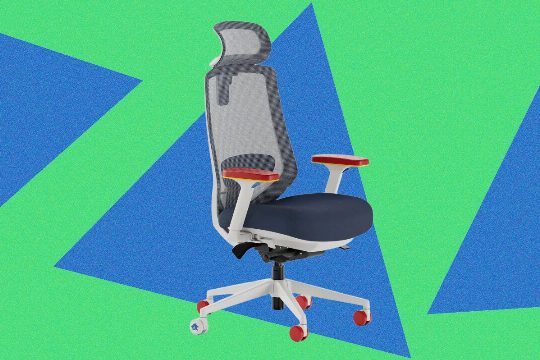
A Sega-edition ergonomic chair offers gamer appeal with office-level ergonomics, but comes with a learning curve.
Coder's cloud development platform suffered an infrastructure compromise, leading to the delivery of malicious Terraform modules containing credential-stealing code.
Hackers used BGP hijacking to deliver malicious updates, affecting Softaculous installations and requiring immediate security measures.
Australian authorities have arrested two alleged TeamPCP hackers responsible for a series of high-profile supply-chain attacks targeting open-source software and developer platforms.
TopResume offers free resume reviews and premium services to help job seekers navigate AI-driven ATS systems and secure employment.
GitHub experienced a worldwide outage affecting multiple services, including API requests, Actions, Pull Requests, and authentication-related services. This guide provides a detailed look at the outage, its impact, and steps to mitigate the effects.
AI coding tools can introduce unvetted or hallucinated open source dependencies faster than traditional security reviews can keep pace.
The Arch Linux project has temporarily disabled adoption of Arch User Repository (AUR) packages after a surge in malicious takeovers of existing packages.