
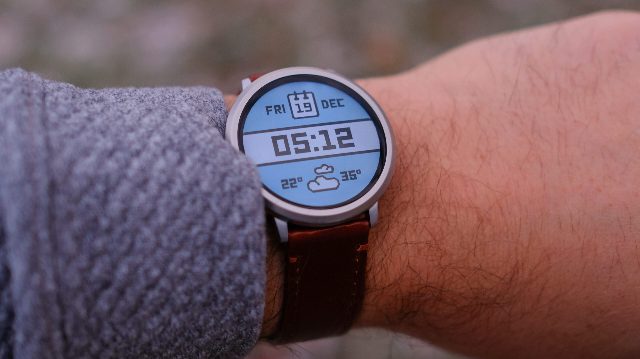
Pebble OS Update: How Plugins Will Supercharge Your Smartwatch
Pebble OS is getting a major update with the addition of plugin support, allowing apps and watchfaces to be more versatile and feature-rich.
Search
Results for "Plugin".
Pebble OS is getting a major update with the addition of plugin support, allowing apps and watchfaces to be more versatile and feature-rich.
A recent compromise of the Rank Math SEO plugin has exposed websites to potential security risks. Here's how to secure your site and prevent future attacks.
Hackers used XSS vulnerabilities in two plugins to install backdoors and create rogue admin accounts, affecting millions of WordPress sites.
Anthropic has just announced a new Claude Marketplace, and it brings all AI-related tools into one place, including plugins, connectors, agents, and more.
Acronis disclosed a high-severity Linux local privilege escalation vulnerability in its backup plugin for cPanel, WebHost Manager (WHM), and Plesk that may be exploited in the wild.
Malicious plugin update compromised over 1,500 WordPress sites, highlighting the importance of security measures.
Hackers are actively exploiting a critical vulnerability in the WooCommerce Wholesale Lead Capture premium plugin for WordPress to upload a PHP backdoor.
An SQL injection vulnerability in the All-in-One WP Migration and Backup plugin for WordPress could allow unauthenticated attackers to execute remote code and take control of affected websites.
A maximum-severity vulnerability in the GiveWP plugin for WordPress allows an unauthenticated attacker to execute arbitrary commands on the hosting server.
A supply-chain hack compromised the BdThemes, a developer of premium WordPress web-design tools, resulting in the creation of rogue admin accounts. This guide provides a detailed explanation of the attack and its implications.
Adobe’s new ChatGPT plugin eliminates app switching by bringing its creative tools under one.
Ukraine's CERT has uncovered attacks distributing an archive containing the legitimate Notepad++ application and a malicious utility called LunchPoke disguised as a plugin to establish persistence.

Threat actors are exploiting an unauthenticated information disclosure vulnerability in the WordPress plugin Gravity SMTP, active on 100,000 sites.

ShapedPlugin's update flow was compromised in a supply chain attack, leading to the distribution of infected releases. This guide provides a detailed overview of the security incident and steps to protect WordPress sites.

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch a maximum-severity flaw in the Widget Factory Joomla Content Editor (JCE) plugin that is being actively exploited in the wild.

At least 15 malicious plugins found on the JetBrains Marketplace were designed to steal AI API keys from developers.

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has given U.S. government agencies three days to secure their servers against an actively exploited vulnerability (CVE-2026-54420) in the LiteSpeed cPanel user-end plugin.

OptinMonster, TrustPulse, and PushEngage WordPress plugins have been compromised in a supply-chain attack affecting Awesome Motive's content distribution network (CDN).

Hackers are exploiting a critical vulnerability in the WP Maps Pro plugin to create rogue administrator accounts on WordPress sites, highlighting the importance of keeping plugins updated.

A selected YouTube video about Artificial Intelligence, with context from OpenAI and a practical checklist before watching.
AI agents are becoming more autonomous and capable, but they also pose significant risks. Learn how to use them safely and protect your data with Gen's Agent Trust Hub.
A recent security breach involving stolen UpdraftCentral keys has exposed thousands of WordPress sites to potential backdoor attacks. Learn how to secure your sites and stay vigilant against such threats.
Learn a quick trick to delete unwanted screenshots using the Nice Shot module in the Good Lock app.
A cross-site request forgery (CSRF) vulnerability in the Elementor plugin for WordPress could allow an unauthenticated attacker to create administrator accounts.
A recently patched critical vulnerability (CVE-2026-32475) in the Elementor Pro plugin for WordPress is being exploited in attacks that deliver a webshell payload and execute arbitrary commands on the server.
Hackers are attempting to exploit two critical authentication bypass vulnerabilities in the miniOrange SAML 2.0 Single Sign On plugin for WordPress that can be used to forge SAML responses and log in as administrators.
A critical vulnerability in the Elementor Pro WordPress plugin could allow attackers to upload executable files for remote code execution on the server.
Hackers are exploiting the "wp2shell" critical vulnerability suite (CVE-2026-63030 and CVE-2026-60137) affecting WordPress Core to deploy persistent webshells and install malicious plugins on affected servers.

OkoBot, a sophisticated malware framework, has been deploying over 20 payloads to steal cryptocurrency wallet seed phrases, credentials, and other sensitive data. This guide provides an in-depth look at the framework's operations and defenses against it.
Intruder built an AI-powered "vulnerability vending machine" that combines code slicing with LLMs to automatically discover complex software vulnerabilities.