
Climate Change Pushes Cryosphere Beyond Safe Operating Space
New research reveals the climate is pushing the cryosphere, including ice, permafrost, and snow, beyond its safe operating space, with grave implications for global stability.
Search
Results for "Push".
New research reveals the climate is pushing the cryosphere, including ice, permafrost, and snow, beyond its safe operating space, with grave implications for global stability.
Next year could usher in an era of optimized foldable phone apps should Google's plans materialize.
Cybersecurity professionals are being targeted with infected security projects on GitHub that deploy a backdoor and information stealer malware. [.
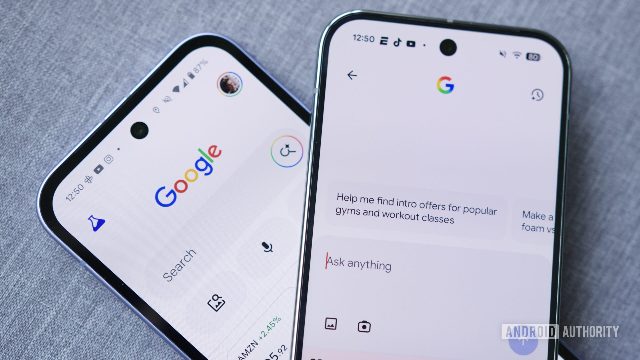
Google was spotted testing Search without AI Mode.
Republicans are intensifying their efforts in historically red Senate seats, facing new challenges as Democrats gain ground in key battleground states.
Skullcandy Push 720 Open earbuds drop to $99.99 on Amazon, with multipoint Bluetooth and up to 30 hours of battery life.
A threat actor uploaded malicious packages to the Arch User Repository (AUR) that impersonated two popular helper tools, yay and paru.
Hackers are abusing legitimate Bing search-result redirects as click URLs in Google search ads to direct users to fake Claude installers that deliver ClickFix attacks.
The Russian state actor Star Blizzard has been using a new malware installation tactic dubbed "RedFlick" to deploy its signature CosmicPulse backdoor.
Custom variants of OpenAI's ChatGPT promoted in sponsored Google results are directing unsuspecting users to malicious sites that use ClickFix attacks to deliver malware.
Google is challenging the EU's demands to open Android to rival AI assistants and share Search data, it could put users' privacy.
An ongoing malware campaign uses SEO-optimized GitHub repositories to impersonate well-known software firms to push a previously undocumented information stealer called Rapuncel.
Hackers compromised HBO Max's official Reddit account and used it to push malicious ads that launched ClickFix attacks to infect Windows and macOS devices with information-stealing malware.
Streaming ad loads jumped 18% this year, and only Prime Video is showing fewer ads than it did.
A new generation of Islamic terror supporters are using AI to spread ‘Slop Jihad’ to new audiences.
Coder's cloud development platform suffered an infrastructure compromise, leading to the delivery of malicious Terraform modules containing credential-stealing code.
Google Search has started showing longer AI Overview summaries for some queries on desktop, including a link to AI.
This week on “Uncanny Valley,” senior writer Will Knight talks his recent visit to China and the future of AI.
A previously unknown malware family dubbed SynkLoader is being distributed in Microsoft Teams phishing campaigns to steal credentials via a fake lock screen.
Hackers compromised the maintainer account behind the widely used Rust crate arrayref to introduce malware that executed on developers' systems during compilation.
A Go-based malware delivered in ClickFix attacks targeting macOS users is stealing cryptocurrency assets, browser-stored passwords, Apple Keychain data, and cached credentials.
Fake Xeno Executor installers are infecting unsuspecting Roblox players with malware that provides remote access and steals sensitive information.
Ads on Instagram, TikTok, and YouTube are painting prescription stimulants in a negative light while promoting supplements for ADHD that lack.
A malvertising campaign on the Bing search service is pushing a fake Claude desktop app installer hosted on a legitimate Claude.ai domain to deliver the SectopRAT malware.
A large-scale operation dubbed 'FakeGit' is pushing SmartLoader and StealC malware through 7,600 malicious GitHub repositories that accumulated more than 14 million downloads.
Two recently disclosed SonicWall SMA1000 vulnerabilities were exploited in zero-day attacks for weeks, allowing threat actors to install custom malware on vulnerable VPN appliances.

The company endorsed landmark AI transparency laws in California and New York last year, but its head of US state and local policy says they may already be.

A financially motivated Russian threat actor tracked as UAT-11795 is using trojanized software to steal credentials and cryptocurrency by deploying a new backdoor called Starland RAT.

Google is pushing Pixel AI beyond the cloud with powerful on-device.

A threat actor has published hundreds of fake GitHub repositories impersonating legitimate software and security projects to distribute infostealer malware.