
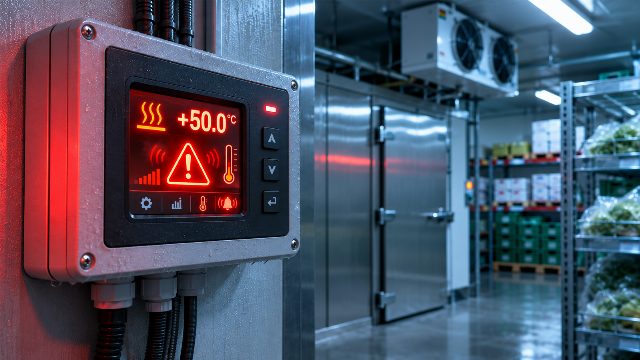
FBI and CISA Warn of Cyberattacks Targeting Refrigeration Systems: A Comprehensive Guide
The FBI and CISA issue a joint warning about cyberattacks on industrial refrigeration systems, emphasizing the need for enhanced cybersecurity measures.
Search
Results for "Targeting".
The FBI and CISA issue a joint warning about cyberattacks on industrial refrigeration systems, emphasizing the need for enhanced cybersecurity measures.
Two Canadians face up to 10 years in prison for hacking US universities and mining cryptocurrency, with multiple universities affected.
Taiwanese network-attached storage (NAS) appliance maker Synology warned customers to update their devices immediately due to a surge in C3RB3r ransomware attacks. [.
Rubedo Life Sciences is developing a topical cream to reduce the appearance of aging by targeting cellular senescence, showing early promise in clinical trials.
WIRED’s Uncanny Valley dives into Elon Musk’s America PAC’s spending strategy and the stakes for AI safety.
Over 150 European politicians, predominantly women, have been featured on harmful deepfake pornography websites, raising concerns about online harassment and intimidation.
The FBI has issued a warning about cybercriminals targeting online accounts, including social media and other platforms, to steal sexually explicit images or videos, which can be used for blackmail or resale.
U.S. federal agencies and South Korea's National Policy Agency warned government and critical infrastructure organizations worldwide to secure their systems against Gunra ransomware attacks.
A new type of malware can worm deep into AI coding systems to steal data and logins—and can flip a “death switch” to destroy files and keep out real.

The Australian Cyber Security Centre (ACSC) issued an alert about a global exploitation campaign targeting vulnerable content management systems (CMS) and plugins.

The U.S. Department of State is offering up to $10 million for information that helps identify or locate members of the UNC5792 and UNC4221 hacker groups, which are linked to Russia's intelligence and military services.

The JDY botnet, a malware network previously associated with Chinese threat actors like Volt Typhoon, has significantly expanded its targeting scope and reconnaissance efforts.

CISA and other US government partners warn of cyberattacks targeting internet-exposed ATG systems used to monitor fuel and liquid storage tanks. Threat actors are compromising and modifying exposed devices through command execution.

The FBI is warning about the Kali365 phishing-as-a-service platform (PhaaS) that is used to hijack Microsoft 365 accounts by abusing OAuth device code authentication to steal session tokens and bypass multi-factor authentication (MFA).
ConnectWise is investigating an active malware campaign targeting managed service providers (MSPs) that uses compromised ScreenConnect environments to deploy rogue remote-access clients, impacting dozens of organizations.
France has linked a series of cyberattacks to Iranian state-backed hackers, causing significant food losses and multiple fires in French supermarkets.
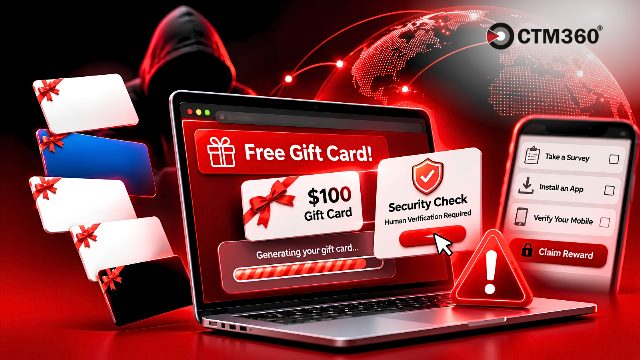
CTM360 exposes a global scam exploiting trusted brands, tricking users into fake reward systems.
France's blood service faces a cyberattack, leading to temperature and defrost settings changes, affecting multiple facilities and threatening stored blood products.
Google updated its policy with an ad-targeting exception for your Gmail and Photos data, and you might not like it.
A large-scale watering hole attack associated with Russian hackers has been targeting iOS and Android users visiting compromised sites or fake ones impersonating legitimate portals. [.
European authorities dismantle a criminal network targeting potential victims worldwide with fraudulent investment schemes.
A think tank aligned with the Trump administration suggests preventing Democrats from holding office, arguing that certain candidates are anti-constitutional. This strategy could face legal challenges.
Anti-oligarchy activists plan to dox high-profile billionaires and their networks, raising $1.2M from wealthy traitors.
FBI confirms North Korean hackers as responsible for the largest cryptocurrency theft, affecting Binance.
Reddit plans to limit access to its full content to logged-in users to combat content scraping and improve ad targeting.
Researchers have uncovered a new Hugging Face malware campaign targeting GPUs for crypto mining, highlighting the evolving threat landscape in the AI space.
Sony ISP subsidiary breached, exposing 2.5 million customer records with personal information, including email addresses and passwords.
Chinese hackers use Silent Train framework to hide zero-day attacks targeting high-value systems, including critical infrastructure.
InfraTrust report highlights critical flaws in network devices, with PHP vulnerabilities posing significant risks.
A Ukrainian national was sentenced to 70 months in prison for his role in ransomware attacks targeting hospitals, government entities, and high-revenue businesses worldwide between 2018 and 2021. [.