
Researchers escape OpenAI Codex sandbox to run commands on host
Researchers escaped OpenAI's Codex sandbox two ways, one running commands on a developer's machine from its most locked-down mode. OpenAI has patched both.
Search
Results for "Researchers".
Researchers escaped OpenAI's Codex sandbox two ways, one running commands on a developer's machine from its most locked-down mode. OpenAI has patched both.
As OpenAI and Anthropic employees grow quieter online, researchers at Chinese AI labs are flocking to X to explain their work, recruit talent, and shape the global conversation.
European researchers are facing significant obstacles in obtaining data from social media platforms like TikTok, hindering their ability to study the impacts of social media on society, despite legal entitlements.

A China-linked threat cluster has been exploiting vulnerable Roundcube servers at U.S. and Canadian universities to steal credentials and deploy backdoor malware.

Multiple weaponized proof-of-concept (PoC) exploits on GitHub were found delivering a Python-based remote access trojan (RAT) named ChocoPoC that can execute commands and steal sensitive data in a campaign believed to target cybersecurity.

The company changed course after researchers spoke out against the policy, which would have covertly limited Claude’s ability to develop competing AI.
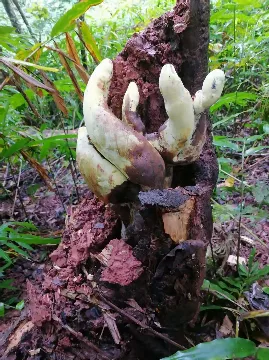
A new species of giant fungus, named Dianjunus rex, has been discovered in China's Yunnan Province. This Ascomycete fungus grows up to 20 inches tall and has no close relatives, illustrating the vast biodiversity of fungi in East Asian forests.
Check Point security gateways were targeted in PHP2Shell attacks that deployed destructive malware on VMware ESXi hosts, raising questions about a possible false-flag operation.
New worm-like malware SCKit targets MSPs, exploiting CVE-2026-84869 to spread from infected devices to MSP technicians' computers and compromise additional networks.
Hackers compromised 4,800 GitHub accounts to steal cloud credentials and secrets, including those from Fortune 100 companies and government entities. The threat actor used malicious workflows to inject stolen data into open-source software ecosystems.
Apache HTTP Server has patched a critical vulnerability in the HTTP/2 module that could allow attackers to execute arbitrary code with server privileges, affecting versions 2.4.55 through 2.4.70 and standalone mod_h2 versions 2.0.8 through 2.0.42.
Security researcher Abdelhamid Naceri has released a new Windows zero-day exploit named SignDrop, which can give attackers SYSTEM privileges by abusing Microsoft's CLFS driver mitigation.
Hackers are increasingly using GSocket, a legitimate remote access tool, to maintain persistent access to Linux servers, even after initial vulnerabilities are patched.
ConnectWise is investigating an active malware campaign targeting managed service providers (MSPs) that uses compromised ScreenConnect environments to deploy rogue remote-access clients, impacting dozens of organizations.
Researchers in Germany gradually reversed human cells’ ages by decades. By doing so, they could track the de-aging process in a way previous rejuvenation experiments could not.
Turla hackers have deployed a new Cereal malware toolset to intercept emails on government Microsoft Exchange servers, according to cybersecurity researchers at ESET.
Recent genetic studies reveal unique dog populations near Chernobyl, raising questions about their evolutionary path and environmental pressures.
Scientists discovered a compound that could help opioid users quit, but the DEA banned it, making research and access difficult.
Fintech platform Sageworks experiences an outage due to suspected cyberattack, impacting borrower-facing features.
Astronomers find a debris disk around a white dwarf, offering clues to our solar system's future.
AI-generated vulnerability reports are overwhelming some bug bounty programs, making it harder for aspiring security researchers to know where to start.
Scientists are replicating a 1960s study on planarian worms that claimed they could learn and transfer memories. The quest to understand this phenomenon continues.
Security researchers at Anthropic have developed an exploit for a critical Linux kernel vulnerability that allows unauthenticated attackers to remotely execute commands as root on servers running Multipath TCP (MPTCP) listeners. [.
A malicious version of Anthropic's Claude Code VS Code extension was distributed through Cursor's marketplace, exposing up to 5,000 developers to malware designed to install persistent SSH backdoors.
Researchers have uncovered a new Hugging Face malware campaign targeting GPUs for crypto mining, highlighting the evolving threat landscape in the AI space.
Prediction market platform Polymarket halts trading after a crypto-draining script breach, with $2.5M traced to a suspected attacker wallet and law enforcement involvement.
Anthropic and OpenAI say they’ve disproved a key tenet of computer science. Researchers are struggling with the fall but also feel like “overexcited bunnies” as they look at new questions to explore.
U.S. law enforcement has shut down Virtualine, a bulletproof hosting service linked to cybercrime, following a multi-national investigation.
Chinese hackers use Silent Train framework to hide zero-day attacks targeting high-value systems, including critical infrastructure.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed two critical PHP vulnerabilities, PHP2Shell, now actively exploited in attacks.