
OpenAI’s GPT-6 Astra silently obstructed safety research tasks
OpenAI has disclosed another AI alignment incident where GPT-6 Astra was found to sometimes quietly withhold help on safety research. [.
Search
Results for "Research".
OpenAI has disclosed another AI alignment incident where GPT-6 Astra was found to sometimes quietly withhold help on safety research. [.
Anthropic and OpenAI say they’ve disproved a key tenet of computer science. Researchers are struggling with the fall but also feel like “overexcited bunnies” as they look at new questions to explore.
I didn’t know I needed this feature, and now I can’t live without it!
Many frontier labs keep their risky research locked away.
Researchers escaped OpenAI's Codex sandbox two ways, one running commands on a developer's machine from its most locked-down mode. OpenAI has patched both.
Anthropic’s CEO says that safety hinges on understanding how AI “thinks.” So far the evidence is.
Jacob Coxon talks to WIRED about the “mini Manhattan project” inside Anthropic, the problem with alignment, and why AI labs have just a few years left to make their systems.
Threat research gives security teams insight into how attackers operate, while MDR turns that intelligence into faster detection and response.
As OpenAI and Anthropic employees grow quieter online, researchers at Chinese AI labs are flocking to X to explain their work, recruit talent, and shape the global conversation.
New studies suggest solar storms could be even more dangerous than previously believed, altering Earth's magnetic field and impacting satellite communications.
European researchers are facing significant obstacles in obtaining data from social media platforms like TikTok, hindering their ability to study the impacts of social media on society, despite legal entitlements.

A China-linked threat cluster has been exploiting vulnerable Roundcube servers at U.S. and Canadian universities to steal credentials and deploy backdoor malware.

Multiple weaponized proof-of-concept (PoC) exploits on GitHub were found delivering a Python-based remote access trojan (RAT) named ChocoPoC that can execute commands and steal sensitive data in a campaign believed to target cybersecurity.

A China-linked espionage campaign targeted exposed REDCap servers to deploy the InfiniteRed malware and steal sensitive data from a medical institution in North America.

The company changed course after researchers spoke out against the policy, which would have covertly limited Claude’s ability to develop competing AI.

Planning trips or degoogling your notes? These fresh AI apps are also worth.

A selected YouTube video about Home Lab, with context from NetworkChuck and a practical checklist before watching.
Japan's Fugaku supercomputer, a critical tool for scientific research, was taken offline after a security breach that compromised user data and credentials.
New Harvard research reveals that 400 hyperscale data centers in the US used as much electricity as the state of Michigan in a single year, highlighting the significant environmental impact of data centers, especially those powered by fossil fuels.
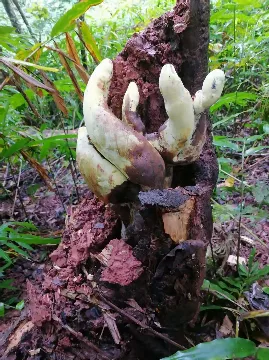
A new species of giant fungus, named Dianjunus rex, has been discovered in China's Yunnan Province. This Ascomycete fungus grows up to 20 inches tall and has no close relatives, illustrating the vast biodiversity of fungi in East Asian forests.
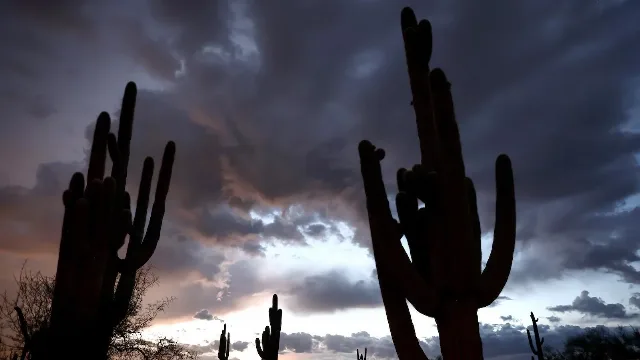
Cacti, once thought to be resilient in arid conditions, are facing new challenges as climate change intensifies drought and other stressors, threatening their survival and the ecosystems they support.
Check Point security gateways were targeted in PHP2Shell attacks that deployed destructive malware on VMware ESXi hosts, raising questions about a possible false-flag operation.
New worm-like malware SCKit targets MSPs, exploiting CVE-2026-84869 to spread from infected devices to MSP technicians' computers and compromise additional networks.
Hackers compromised 4,800 GitHub accounts to steal cloud credentials and secrets, including those from Fortune 100 companies and government entities. The threat actor used malicious workflows to inject stolen data into open-source software ecosystems.
Hackers are actively exploiting newly disclosed N-able N-central zero-day vulnerabilities, including 4EverAble2Shell, to compromise servers and deploy cryptocurrency miners.
Apache HTTP Server has patched a critical vulnerability in the HTTP/2 module that could allow attackers to execute arbitrary code with server privileges, affecting versions 2.4.55 through 2.4.70 and standalone mod_h2 versions 2.0.8 through 2.0.42.
New research reveals the climate is pushing the cryosphere, including ice, permafrost, and snow, beyond its safe operating space, with grave implications for global stability.
Security researcher Abdelhamid Naceri has released a new Windows zero-day exploit named SignDrop, which can give attackers SYSTEM privileges by abusing Microsoft's CLFS driver mitigation.
Hackers are increasingly using GSocket, a legitimate remote access tool, to maintain persistent access to Linux servers, even after initial vulnerabilities are patched.
ConnectWise is investigating an active malware campaign targeting managed service providers (MSPs) that uses compromised ScreenConnect environments to deploy rogue remote-access clients, impacting dozens of organizations.